 FTPeach
SFTP connections
Use SFTP when your provider gives you SSH file access. You can sign in with an account password or a private SSH key. SFTP is a different connection type from FTPS: select the one your server actually provides.
On this page
Before you connect
Ask your provider or server administrator for:
- The server hostname or IP address and its SSH port.
- Your username and whether the account uses a password or a key.
- The server's expected host-key fingerprint, given to you some other way than over this connection.
- The folder you should work in and whether you may upload or replace files there.
Three different secrets or identities can be involved:
| Item | What it is for |
|---|---|
| Account password | Signing in to the server as your username. |
| Your private key and its passphrase | Proving your account identity instead of using the account password. The passphrase unlocks the key file. |
| Server host-key fingerprint | Checking that the server is the one you meant to reach. This is not your account's SSH key. |
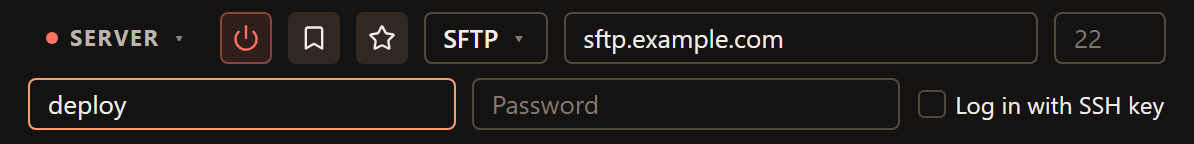
Connect with a password
- Open the source menu at the top of a pane and choose Server.
- Choose SFTP in the protocol selector.
- Enter Address and Username. The suggested port is 22; enter a different Port if your provider specifies one.
- Leave Log in with SSH key off and enter your account Password.
- Select Connect, then verify the server if prompted.
Connect with an SSH key
First arrange for the matching public key to be authorized for your server account. Selecting a file in FTPeach does not grant that account access.
- Choose SFTP and enter the same address, port and username as above.
- Turn on Log in with SSH key. This replaces the password field with the key controls and clears the account password from the form.
- Select the key-shaped Key file button and choose your private key file.
Do not choose its public
.pubfile. - Enter the key's Passphrase if it has one; otherwise leave that field empty.
- Select Connect, then check the server fingerprint if prompted.
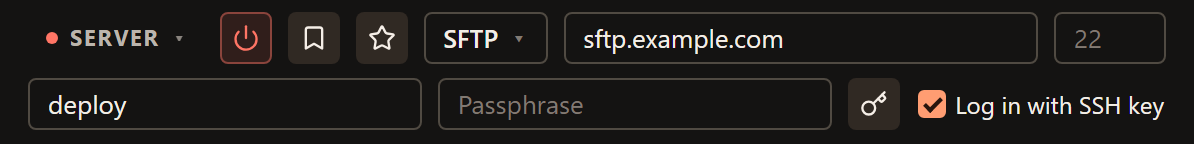
The key button opens a file picker. The passphrase belongs to that file, not to your server account or the FTPeach password vault.
Choosing a key file
FTPeach can read OpenSSH private-key files containing Ed25519, RSA or
ECDSA P-256 keys, including passphrase-protected files. OpenSSH is the file format; Ed25519,
RSA and ECDSA are key types. A filename extension alone does not identify either.
An OpenSSH private-key file starts with -----BEGIN OPENSSH PRIVATE KEY-----.
For a new key, prefer Ed25519 when your administrator supports it. FTPeach shows a warning when it recognizes a selected RSA private key because RSA signing has a known timing weakness. The warning is not a rejection of the key.
If your supplied key cannot be read, confirm its format and passphrase with the administrator. Renaming its extension does not convert it. Keep the original if you export a copy in another format.
Verify the server
On a first connection, the default settings stop sign-in until you confirm the server's host key. Compare the offered fingerprint with the one supplied by your administrator. If it matches, choose Trust this server; FTPeach retries the connection. If you cannot verify it, cancel and ask the administrator first.
A later change to the host key stops the connection too. The confirmation shows the previously trusted fingerprint and the newly offered one. A server reinstall can explain a change, but do not assume that is the cause. Verify the new fingerprint independently before choosing Trust the new key.
When SFTP does not connect
| Message | What to check |
|---|---|
| Incorrect username or password | Confirm the username and whether the account expects a password or a key. For key login, ask whether the matching public key is authorized for that account. |
| Couldn't read the key — the file is corrupted or the passphrase is incorrect. | Select the private file again, check its format and use its passphrase rather than the account password. |
| The key or certificate file was not found | The file may have moved or its drive may be unavailable. Select it again from its current location. |
| The server's host key has changed, so FTPeach didn't connect. | Follow the fingerprint checks above before trusting a replacement key. |
| The server and FTPeach have no SSH algorithm in common. | Ask the administrator to check the server's SSH configuration and compatibility. |
| Connection refused / Server is not responding | Confirm the SSH port, server availability and any VPN or network access requirements. See the connection checklist. |
Once connected
Open the folder your provider named, then try a small file using Your first transfer. If signing in works but a file operation is denied, check the folder and account permissions with the administrator; signing in does not mean you can write to every folder.
For repeat connections, save a bookmark. If you carry keys on a removable drive, read about portable key files. For editing files directly from a server pane, see Editing remote files.