 FTPeach
FTPS connections
FTPS is FTP protected by TLS. Choose it when your provider offers explicit FTPS, also called FTP with explicit TLS. It is different from SFTP, which uses SSH and a server host key instead of a TLS certificate.
FTPeach supports explicit FTPS, but does not support implicit FTPS. If your provider specifies implicit FTPS, ask for an explicit FTPS endpoint or another supported protocol. Changing a port number alone does not change the server's mode.
On this page
Connect with explicit FTPS
Ask your provider for the FTPS hostname, port, username, password and destination folder. If the service uses a private certificate authority, ask for its CA certificate too.
- Open the source menu at the top of a pane and choose Server.
- Choose FTPS, then enter Address. Use the hostname your provider gave you for the certificate, rather than substituting a different name.
- The suggested Port is 21. Enter another port if the provider specifies it.
- Fill in Username and Password. Leave Verify certificate checked.
- Select Connect. Once the folder listing loads, open your destination folder.
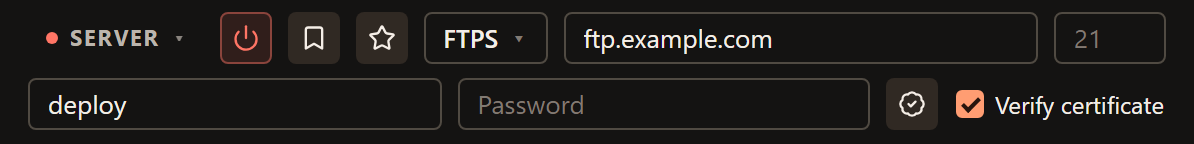
The badge-shaped button beside the password field selects a CA certificate. Most public services do not require you to choose a separate file.
Verify the certificate
With Verify certificate enabled, FTPeach rejects a certificate it cannot validate. Treat the error as a reason to check the hostname and certificate with the provider, rather than immediately disabling verification.
For a private certificate authority:
- Get the CA certificate in PEM format from the administrator. This is a certificate, not a private key or an account password.
- Keep Verify certificate enabled and select CA certificate in the connection form. Choose the file you received.
- Connect again. If verification still fails, ask the administrator to check the certificate chain, hostname and validity dates.
Unchecking Verify certificate allows invalid certificates and disables the CA-file button. The connection still uses TLS, but that is no substitute for checking the server's identity.
When FTPS does not connect
| Message or symptom | What to check |
|---|---|
| The server's certificate isn't valid. | Check the hostname and certificate with the provider. For a private CA, use the trusted CA file as described above. |
| Couldn't set up encryption (TLS) with the server. | Confirm that the endpoint supports explicit FTPS and that you used its correct port. An implicit-only service is unsupported. |
| Incorrect username or password. | Confirm the account details and that the account is allowed to use this service. |
| The key or certificate file was not found | Select the CA certificate again if it has moved or its drive is unavailable. |
| Sign-in works, but files do not list or transfer | FTPS also uses FTP data connections. Check passive and active mode with the administrator. |
Do not switch to plain FTP to dismiss a TLS error: that changes the connection's protection. Confirm the correct service with your provider instead.
Once connected, try a small first transfer, then save a bookmark for next time. For interrupted jobs, see Transfers and files.